The General Data Protection Regulation & The Duty to use Encryption

The General Data Protection Regulation, abbreviated to GDPR, raised a storm when it arrived. In reality, it merely tightened up on existing good practice according to digital security specialists Gemalto. The right to withhold consent and to be forgotten has always been there, for example. However, the GDPR brings a free enforcement service for consumers, thus avoiding the need for third party, paid assistance.

The GDPR Bottom Lines for Data Security
Moreover, the GDPR has penalties it can apply, of the order that might have a judge choking on his wig. Under it, data security measures such as pseudonymisation (substitution of identifying fields) and encryption (encoding including password protection) have become mandatory. Businesses must further respect their client data by:

a) Storing it in a secure environment supported by robust services and systems

b) Having proven measures to restore availability and access after a breach

c) Being able to prove frequent effectiveness testing of these measures.

The General Data Protection Regulation places an onus on businesses to report any data breaches. This places us in a difficult situation. We must either face at least a wrist slap upon reporting failures. Alternatively, pay a fine of up to ?10 million, or 2% of total worldwide annual turnover.

The Engineered Weak Link in the System
Our greatest threat of breach is probably when the data leaves our secure environment, and travels across cyberspace to an employee, stakeholder, collaborator, or the client themselves. Since email became open to attack, businesses and individuals have turned to sharing platforms like Dropbox, Google Drive, Skydrive, and so on. While these do allow an additional layer of password protection, none of these has proved foolproof. The GDPR may still fine us heavily, whether or not we are to blame for the actual breach.

How Hacking is Approaching Being a Science
We may make a mistake we may regret, if we do not take hacking seriously. The 10 worst data hacks Identity Force lists are proof positive that spending lots of money does not guarantee security (any more than having the biggest stock of nuclear weapons). We have to be smart, and start thinking the way that hackers do.

Hacker heaven is finding an Experian or a Dun & Bradstreet that may have shielded 143 million, and 33 million consumer records respectively, behind a single, flimsy cyber-security door. Ignorance is no excuse for them. They should simply have known better. They should have rendered consumer data unreadable at individual record level. The hackers could have found this too demanding to unpick, and have looked elsewhere.

How Data Encryption Can Help Prevent Hackers Succeeding
Encrypting data is dashboard driven, and businesses need not concern themselves about it works. There are, however, a few basic decisions they must take:

a) Purge the database of all information held without explicit permission

b) Challenge the need for the remaining data and purge the nice-to-haves

c) Adopt a policy of encrypting access at business and customer interfaces

d) Register with three freemium encryption services that seem acceptable

e) After experimenting, sign up for a premium service and be prepared to pay

Factors to Consider When Reaching a Decision
Life Hacker?suggests the following criteria although the list is a one-size-fits-all

a) Is the system fast, simple, and easy to operate

b) Can you encrypt hidden volumes within volumes

c) Can you mass-encrypt a batch of files easily

d) Do all other files remain encrypted when you open one

e) Do files automatically re-encrypt when you close them

f) How confident are you with the vendor, on a scale of 1 to 10

It may be wise to encrypt all the files on your system, and not just your customer data. We are always open to a hack by the competition after our strategic planning. If we leave the decision up to IT, then IT, being human may take the easy way out, and encrypt as little as possible.

Contact Us

  • (+353)(0)1-443-3807 – IRL
  • (+44)(0)20-7193-9751 – UK

Check our similar posts

Solutions to Password Overload

If only technologists had their way, passwords and PINs would have long been replaced with more innovative (and admittedly, better) security solutions. But such is not the case. Those alternative solutions, which include biometrics, smart cards, and password fobs, effective as they may be, are just way too expensive to implement.

So although passwords and PINs may not be here to stay, they certainly won’t be going away soon either.

Why keeping passwords in memory is no longer possible

A couple of decades ago, it would have been nearly impossible to crack an eight-character password using brute force. Today, however, advancements in computing power are rendering the typical passwords of the past easily decipherable, forcing us to come up with passwords that are not only much longer, but also much more complex and hence difficult to recall.

For instance, memorable words like your favourite character (e.g. ‘skywalker’) may have been acceptable then, but not anymore. Today?s security systems will encourage you to insert numbers or even other keyboard characters as a means to once again counter brute force. Hence, ‘sk5%ywa936lker@#’ may be more acceptable.

Remembering that one alone can be pretty daunting.

To further complicate matters, the number of applications that require passwords for access is much greater than before even for a single end user. Ordinary end users have to keep track of passwords for their email account, network login, workstation login, online services, and so on.

The burden is even greater for your IT admins, who have to remember a larger collection of passwords that protect business critical systems and applications. Clearly, the team in charge of your IT security will need a way to manage all these passwords.

Password management solutions

Existing password management solutions typically come in the form of software applications that store passwords. Basically, all you need to remember are your login details for the app a.k.a. the ?master password?. Once you’ve gained access inside, you can then retrieve any password you stored there.

Some of these apps are installed in portable devices like Pocket PCs, PDAs, or smartphones, which you would normally take along with you. For as long as the device stays with you, your passwords will be in safe hands. What’s more, you can retrieve them anywhere you go.

But obviously, there’s a problem. What if the device gets misplaced or stolen? Although the person who ends up with your device may not be able to gain access into the app and your passwords, neither will you. A better solution would therefore be an app that can be accessed anywhere but is not susceptible to getting lost.

Web-based password manager

A web-based password manager fits the bill. You don’t have to take it with you, but still you can access it almost anywhere. A typical web-based password manager will have all your passwords stored in a centralised, highly secure location.

If you want, you can even use your mobile password manager along with the web-based one. Ideally, your web-based password manager would have a copy of all the end-user passwords as well as the master passwords of your organisation.

With an easy to access but highly-secure web-based password manager, you no longer have to come up with passwords that (ironically) are supposed to be easy to remember but hard to crack at the the same time.

Furthermore, password managers are ideal for keeping passwords that have to be changed every-now-and-then; a requirement that’s becoming all too common in organisations bent on enforcing more stringent controls.

ESOS ? Why we must have it

The 9,000 big UK businesses directly affected by the new Energy Saving Opportunity Scheme could save UK?250 million between them, or an average UK?27,000 each, if they reduced electricity consumption by just 1%. The total amount is equal to the output of five power stations, at a time when Britain?s grid is under strain.
On 26 November 2014, UK Energy and Climate Change Secretary Ed Davey met with over 100 opinion makers from businesses, charities and universities at the Institute of Directors. The gist of what he presented was:

  • ?Britain?s big firms are spending around ?2.8 billion extra each year on inefficient energy technologies ? the equivalent output of nearly five power stations;
  • Now is the time to seize the opportunity with ESOS ? and organisations up and down the country are already gearing up to make changes to save energy, save money and save the environment.
  • If business did what business is supposed to do [that is innovate to make money] and act and invest, it will save ? and that’s the bottom line.?

The environmental benefits are as important although EcoVaro agrees with Ed Davey for taking a pecuniary approach. Businesses above the threshold of 250 staff and a balance sheet of UK?34 million would have not achieved their status unless they spent their money wisely.
The discussion panel included Rhian Kelly (Director of Business Environment at CBI), and Paul Ekins (Director UCL Institute for Sustainable Resources & Deputy Director of the UK Energy Research Centre). Hugh Jones, Managing Director, Advisory at the Carbon Trust responded to Ed Davey?s remarks by commenting:

  • ?At the Carbon Trust we have already engaged with hundreds of businesses on ESOS, helping to explain how they can achieve compliance while also making significant energy savings and cutting carbon.
  • Businesses often aren’t aware of opportunities in energy efficiency, or they don’t realise how attractive the paybacks can be. By requiring companies to understand exactly how they can make cost-effective investment in energy efficiency, they are far more likely to take action.
  • From the interest we have seen so far we expect ESOS to benefit British business by helping companies to reduce overheads and increase competitiveness.

The UK?s Energy Saving Opportunity Scheme ESOS is a gold mine of opportunities for big business, the environment and the population that breathes the air. Measurement of critical energy throughputs is the beginning of the process. EcoVaro is standing by to help you convert your data to meaningful information.

What Is Technical Debt? A Complete Guide

You buy the latest iPhone on credit. Turn to fast car loan services to get yourself those wheels you’ve been eyeing for a while. Take out a mortgage to realise your dream of being a homeowner. Regardless of the motive, the common denominator is going into financial debt to achieve something today, and pay it off in future, with interest. The final cost will be higher than the loan value that you took out in the first place. However, debt is not limited to the financial world.

Technical Debt Definition

Technical debt – which is also referred to as code debt, design debt or tech debt – is the result of the development team taking shortcuts in the code to release a product today, which will need to be fixed later on. The quality of the code takes a backseat to issues like market forces, such as when there’s pressure to get a product out there to beat a deadline, front-run the competition, or even calm jittery consumers. Creating perfect code would take time, so the team opts for a compromised version, which they will come back later to resolve. It’s basically using a speedy temporary fix instead of waiting for a more comprehensive solution whose development would be slower.

How rampant is it? 25% of the development time in large software organisations is actually spent dealing with tech debt, according to a multiple case study of 15 organizations. “Large” here means organizations with over 250 employees. It is estimated that global technical debt will cost companies $4 trillion by 2024.

Is there interest on technical debt?

When you take out a mortgage or service a car loan, the longer that it takes to clear it the higher the interest will be. A similar case applies to technical debt. In the rush to release the software, it comes with problems like bugs in the code, incompatibility with some applications that would need it, absent documentation, and other issues that pop up over time. This will affect the usability of the product, slow down operations – and even grind systems to a halt, costing your business. Here’s the catch: just like the financial loan, the longer that one takes before resolving the issues with rushed software, the greater the problems will pile up, and more it will take to rectify and implement changes. This additional rework that will be required in future is the interest on the technical debt.

Reasons For Getting Into Technical Debt

In the financial world, there are good and bad reasons for getting into debt. Taking a loan to boost your business cashflow or buy that piece of land where you will build your home – these are understandable. Buying an expensive umbrella on credit because ‘it will go with your outfit‘ won’t win you an award for prudent financial management. This also applies to technical debt.

There are situations where product delivery takes precedence over having completely clean code, such as for start-ups that need their operations to keep running for the brand to remain relevant, a fintech app that consumers rely on daily, or situations where user feedback is needed for modifications to be made to the software early. On the other hand, incurring technical debt because the design team chooses to focus on other products that are more interesting, thus neglecting the software and only releasing a “just-usable” version will be a bad reason.

Some of the common reasons for technical debt include:

  • Inadequate project definition at the start – Where failing to accurately define product requirements up-front leads to software development that will need to be reworked later
  • Business pressure – Here the business is under pressure to release a product, such as an app or upgrade quickly before the required changes to the code are completed.
  • Lacking a test suite – Without the environment to exhaustively check for bugs and apply fixes before the public release of a product, more resources will be required later to resolve them as they arise.
  • Poor collaboration – From inadequate communication amongst the different product development teams and across the business hierarchy, to junior developers not being mentored properly, these will contribute to technical debt with the products that are released.
  • Lack of documentation – Have you launched code without its supporting documentation? This is a debt that will need to be fulfilled.
  • Parallel development – This is seen when working on different sections of a product in isolation which will, later on, need to be merged into a single source. The greater the extent of modification on an individual branch – especially when it affects its compatibility with the rest of the code, the higher the technical debt.
  • Skipping industrial standards – If you fail to adhere to industry-standard features and technologies when developing the product, there will be technical debt because you will eventually need to rework the product to align with them for it to continue being relevant.
  • Last-minute product changes – Incorporating changes that hadn’t been planned for just before its release will affect the future development of the product due to the checks, documentation and modifications that will be required later on

Types of Technical Debt

There are various types of technical debt, and this will largely depend on how you look at it.

  • Intentional technical debt – which is the debt that is consciously taken on as a strategy in the business operations.
  • Unintentional technical debt – where the debt is non-strategic, usually the consequences of a poor job being done.

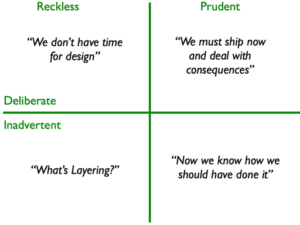
This is further expounded in the Technical Debt Quadrant” put forth by Martin Fowler, which attempts to categorise it based on the context and intent:

Technical Debt Quadrant

Source: MartinFowler.com

Final thoughts

Technical debt is common, and not inherently bad. Just like financial debt, it will depend on the purpose that it has been taken up, and plans to clear it. Start-ups battling with pressure to launch their products and get ahead, software companies that have cut-throat competition to deliver fast – development teams usually find themselves having to take on technical debt instead of waiting to launch the products later. In fact, nearly all of the software products in use today have some sort of technical debt.

But no one likes being in debt. Actually, technical staff often find themselves clashing with business executives as they try to emphasise the implications involved when pushing for product launch before the code is completely ready. From a business perspective, it’s all about weighing the trade-offs, when factoring in aspects such as the aspects market situation, competition and consumer needs. So, is technical debt good or bad? It will depend on the context. Look at it this way: just like financial debt, it is not a problem as long as it is manageable. When you exceed your limits and allow the debt to spiral out of control, it can grind your operations to a halt, with the ripple effects cascading through your business.


Ready to work with Denizon?