User-Friendly RASCI Accountability Matrices

Right now, you’re probably thinking that’s a statement of opposites. Something dreamed up by a consultant to impress, or just to fill a blog page. But wait. What if I taught you to create order in procedural chaos in five minutes flat? ?Would you be interested then?

The first step is to create a story line ?

Let’s imagine five friends decide to row a boat across a river to an island. Mary is in charge and responsible for steering in the right direction. John on the other hand is going to do the rowing, while Sue who once watched a rowing competition will be on hand to give advice. James will sit up front so he can tell Mary when they have arrived. Finally Kevin is going to have a snooze but wants James to wake him up just before they reach the island.

That’s kind of hard to follow, isn’t it ?

Let’s see if we can make some sense of it with a basic RASCI diagram ?

Responsibility Matrix: Rowing to the Island
Activity Responsible Accountable Supportive Consulted Informed
Person John Mary Sue James Kevin
Role Oarsman Captain Consultant Navigator Sleeper

?

Now let’s add a simple timeline ?

Responsibility Matrix: Rowing to the Island
? Sue John Mary James Kevin
Gives Direction ? ? A ? ?
Rows the Boat ? R ? ? ?
Provides Advice S ? ? ? ?
Announces Arrival ? ? A C ?
Surfaces From Sleep ? ? ? C I
Ties Boat to Tree ? ? A ? ?

?

Things are more complicated in reality ?

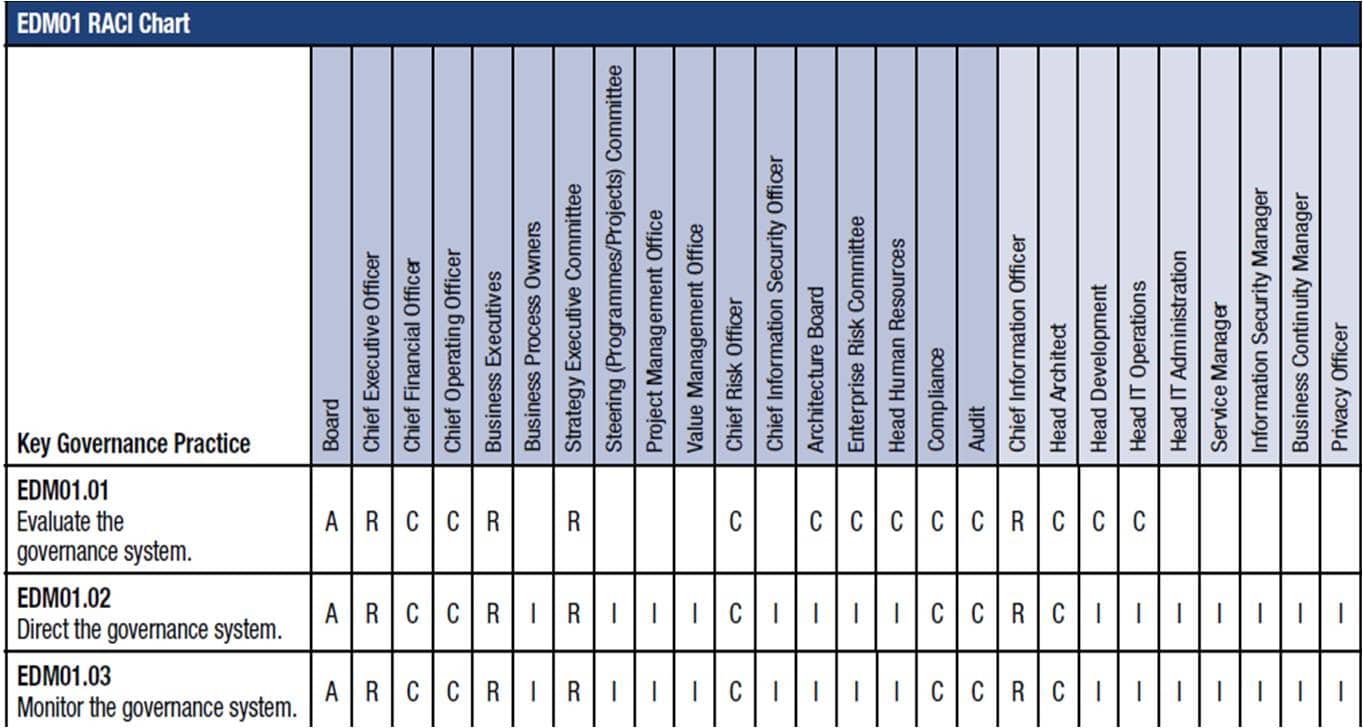
Quite correct. Although if I had jumped in at the detail end I might have lost you. Here?s a more serious example.

rasci

?

There?s absolutely no necessity for you so examine the diagram in any detail, other to note the method is even more valuable in large, corporate environments. This one is actually a RACI diagram because there are no supportive roles (which is the way the system was originally configured).

Other varieties you may come across include PACSI (perform, accountable, control, suggest, inform), and RACI-VS that adds verifier and signatory to the original mix. There are several more you can look at Wikipedia if you like.

Check our similar posts

Systems Integration as a means to cost reduction

System integration in an organisation refers to a process whereby two or more separate systems are brought together for the purpose of pooling the value in the separate systems into one main system. A key component of process consolidation within any organisation is the utilisation of IT as a means to achieve this end. As such, system integration as a means to cost reduction offers organisations the opportunity to adopt and implement lean principles with the attendant benefits. The implementation of lean techniques requires an adherence to stated methods to facilitate the elimination of wastage in the production of goods and services. In summary, the lean philosophy seeks to optimise the speed of good and service production, through the elimination of waste.

While analysing some of the traditional sources of waste in organisational activities, things like overproduction, inventory, underutilised ideas, transmission of information and ideas, transportation of people and material, time wastage and over-processing stand out. The fact is that companies can eliminate a significant portion of waste through the utilisation of IT to consolidate processes within their organisation.

Adopting lean principles calls for the identification of all of the steps in the company value stream for each product family for the purpose of the eliminating the steps that do not create any value. In other words, this step calls for the elimination of redundant steps in the process flow. This is exactly what the utilisation of IT to consolidate processes offers a company. For instance, the adoption of a central cloud system across a large organisation with several facilities could increase efficiencies in that company. Such a company would drastically reduce the redundancies that used to exist in the different facilities, eliminate the instances of hardware and software purchase, maintenance and upgrade, modernise quality assurances processes and identify further opportunities for improvement.

Perhaps, from the company’s point of view, and from the perspective of lean process implementation, the most important factor is?the effect it has?on the bottom line.’reducing the number of hardware, eliminating the need for maintaining and upgrading hardware, removing the necessity for software purchase and upgrade across facilities also contributes to a significant reduction in operational costs.?This reduction in the cost of operations leads to a corresponding increase in the profit margin of the company.

Applying system integration as a means to cost reduction can also lead to the reduction in the number of people needed to operate the previous systems that have been integrated into one primary unit. Usually, companies must hire people with specialised knowledge to operate and maintain the various systems. Such employees must also receive special training and frequent ongoing education to constantly stay informed of the latest trends in process management. With the integration of the system, the number of people needed to maintain the central system will be significantly reduced, also improving the security of information and other company trade secrets.

Based on an analysis of the specific needs that exist in a particular company environment, a system integration method that is peculiar to the needs of that organisation will be worked out. Some companies may find it more cost-effective to use the services of independent cloud service providers. Others with more resources and facilities may decide to set up their own cloud service systems. Often, private cloud service system capabilities far exceed the requirements of the initiating company, meaning that they could decide to “sell” the extra “space” on their cloud network to other interested parties.

A company that fully applies the lean principles towards the integration of its systems will be able to take on additional tasks as a result of the system consolidation. This leads to an increase in performance, and more efficiency due to the seamless syncing of information in a timely and uniform manner.

Companies have to combine a top-down and a bottom-up approach towards their system integration methods. A top-down approach simply utilises the overall system structure that is already in place as a starting point, or as a foundation. The bottom-up approach seeks to design new systems for integration into the system. Other methods of system integration include the vertical, star and horizontal integration methods. In the horizontal method, a specified subsystem is used as an interface for communication between other subsystems. For the star system integration method, the subsystems are connected to the system in a manner that resembles the depiction of a star; hence, the name. Vertical integration refers to the method of the integration of subsystems based on an analysis of their functionality.

The key to successful system integration for the purpose of cost reduction is to take a manual approach towards identifying the various applicable lean principles, with respect to the system integration process. For instance, when value has been specified, it becomes easier to identify value streams. The other process of removing unnecessary or redundant steps will be easier to follow when the whole project is viewed from the whole, rather than’the part. Creating an integrated system needs some?patience?in order to work out kinks and achieve the desired perfect value that creates no waste.

Contact Us

  • (+353)(0)1-443-3807 – IRL
  • (+44)(0)20-7193-9751 – UK
Spreadsheet Woes – Burden in SOX Compliance and Other Regulations

End User Computing (EUC) or end User Developed Application (UDA) systems like spreadsheets used to be ideal ad-hoc solutions for data processing and financial reporting. But those days are long gone.

Today, due to regulations like the:

  • Sarbanes-Oxley (SOX) Act,
  • Dodd-Frank Act,
  • IFRS (International Financial Reporting Standards),
  • E.U. Data Protection Directive,
  • Basel II,
  • NAIC Model Audit Rules,
  • FAS 157,
  • yes, there?s more ? and counting

a company can be bogged down when it tries to comply with such regulations while maintaining spreadsheet-reliant financial and information systems.

In an age where regulatory compliance have become part of the norm, companies need to enforce more stringent control measures like version control, access control, testing, reconciliation, and many others, in order to pass audits and to ensure that their spreadsheets are giving them only accurate and reliable information.

Now, the problem is, these control measures aren’t exactly tailor-made for a spreadsheet environment. While yes, it is possible to set up a spreadsheet and EUC control environment that utilises best practices, this is a potentially expensive, laborious, and time-consuming exercise, and even then, the system will still not be as foolproof or efficient as the regulations call for.

Testing and reconciliation alone can cost a significant amount of time and money to be effective:

  1. It requires multiple testers who need to test spreadsheets down to the cell level.
  2. Testers will have to deal with terribly disorganized and complicated spreadsheet systems that typically involve single cells being fed information by other cells in other sheets, which in turn may be found in other workbooks, or in another folder.
  3. Each month, an organisation may have new spreadsheets with new links, new macros, new formulas, new locations, and hence new objects to test.
  4. Spreadsheets rarely come with any kind of supporting documentation and version control, further hampering the verification process.
  5. Because Windows won’t allow you to open two Excel files with the same name simultaneously and because a succession of monthly-revised spreadsheets separated by mere folders but still bearing the same name is common in spreadsheet systems, it would be difficult to compare one spreadsheet with any of its older versions.

But testing and reconciliation are just two of the many activities that make regulatory compliance terribly tedious for a spreadsheet-reliant organisation. Therefore, the sheer intricacy of spreadsheet systems make examining and maintaining them next to impossible.

On the other hand, you can’t afford not to take these regulations seriously. Non-compliance with regulatory mandates can have dire consequences, not the least of which is the loss of investor confidence. And when investors start to doubt the management’s capability, customers will start to walk away too. Now that is a loss your competitors will only be too happy to gain.

Learn more about our server application solutions and discover a better way to comply with regulations.

More Spreadsheet Blogs


Spreadsheet Risks in Banks


Top 10 Disadvantages of Spreadsheets


Disadvantages of Spreadsheets – obstacles to compliance in the Healthcare Industry


How Internal Auditors can win the War against Spreadsheet Fraud


Spreadsheet Reporting – No Room in your company in an age of Business Intelligence


Still looking for a Way to Consolidate Excel Spreadsheets?


Disadvantages of Spreadsheets


Spreadsheet woes – ill equipped for an Agile Business Environment


Spreadsheet Fraud


Spreadsheet Woes – Limited features for easy adoption of a control framework


Spreadsheet woes – Burden in SOX Compliance and other Regulations


Spreadsheet Risk Issues


Server Application Solutions – Don’t let Spreadsheets hold your Business back


Why Spreadsheets can send the pillars of Solvency II crashing down

?

Advert-Book-UK

amazon.co.uk

?

Advert-Book-USA

amazon.com

Contact Us

  • (+353)(0)1-443-3807 – IRL
  • (+44)(0)20-7193-9751 – UK
Authentication and Access Control

Threats to your data can come from external or internal sources.

  1. There are individuals who don’t have the authorisation but are driven by malicious intentions to gain access to certain information. This may refer to individuals who already belong to your organisation (but don’t have the necessary access rights) as well as those who don’t.
  2. There are individuals who have both the authorisation and, unfortunately, the malicious intentions over certain information.
  3. Finally, there are individuals who have the authorisation, no malicious intentions, but have accidentally exposed the information in question to those without the proper authority.

While curbing threats 2 and 3 would require other methods, threat #1 can be countered if the right authentication and access control systems are in place.

Here’s what we can do for you:

  • Work with your key personnel to determine who gets access to what.
  • Help you decide whether a single factor or a two-factor authentication (2FA) is appropriate for your organisation and recommend which factors are most suitable. Login methods may include but are not limited to the following:
    • biometric devices
    • Kerberos tickets
    • mobile phones
    • passwords
    • PKI certificates
    • proximity cards
    • smart cards
    • tokens
  • Install the necessary infrastructure needed for the factors chosen. For instance, if you opt to use biometrics, then biometric scanners will be installed. We’ll make sure that the authentication terminals are situated in places where achieving optimal traffic and work flow has been taken into consideration.

Other defences we’re capable of putting up include:

Ready to work with Denizon?