A Definitive List of the Business Benefits of Cloud Computing ? Part 3

Strengthens business continuity/disaster recovery capabilities

Today’s business landscape calls for companies to have reliable business continuity and disaster recovery capabilities. After all, when the system goes down, customers and even employees would rarely ask ‘why‘ or ‘what happened‘ but instead go directly to the ‘how soon can we get back up‘ part.

So unless they’ve been struck by the same unforeseen disaster your business is also experiencing, a couple of hours downtime is plenty enough for most of these people. What’s worse is when they simply don’t wait until they get access again and just go to other providers that can offer the same services. In short, your inability to provide continuous IT and business services could translate to lost opportunities which your competition would only be too willing to gain. And that’s not even counting the possibility of losing essential data and other potential negative impact that critical IT failure can bring about.

The answer to avoiding such a scenario is of course, having a sound business continuity and disaster recovery plan in place. But this is actually easier said than done.

Traditionally, setting up a business continuity plan entailed some tedious procedures in addition to very costly infrastructure. We’re talking here about acquiring and maintaining practically a replication of the hardware infrastructure and environments currently existing for business-critical systems and data. Note that these mirror systems should be set-up, housed, and maintained in a remote facility or location.

Making the deployment even more complex is the constant need to update the data in storage as well as keep software applications in sync between the system in use and the one on standby mode. This process would involve the physical transfer of data and syncing of applications, which is cumbersome and again, expensive.

While large enterprises would not even think twice about having to spend so much to ensure that operations would never come to a grinding halt, most small and mid-sized organisations would not have the required financial means for them to even start considering this option. Often, the bulk of their disaster recovery plan would simply consist of some tape backups, and a lot of hoping that they would never have to suffer from any outage or IT failure.

But all that can be changed with the arrival of cloud computing.

A cloud strategy offers an affordable solution for business continuity and disaster recovery for SMBs with limited resources and even big companies trying to minimise expenses by looking for alternative options.

A reliable service provider would already have the required infrastructure and software vital to a viable BC/DR plan and complete with the appropriate security measures. Organisations need not spend upfront for these facilities, but get to benefit from having updated data backup and a virtualised mirror system that would allow them to quickly get back up in the event of an outage or catastrophic disaster.

When looking to the cloud for a cost-effective BC/DR plan however, it’s worth keeping in mind that not all cloud providers are created equal. That’s why businesses also have many important factors to take into account before signing cloud contracts.

Yes, provision for continuity and and taking necessary precautions against outages are inherent in the cloud service itself, but you’d be surprised how many of these providers don’t actually take responsibility for service interruption. To give organisations some assurance of the cloud company’s capacity for continued service, contracts should stipulate availability guarantees and liability for downtime that the provider is willing to answer for.

Once these relevant issues are ironed out however, it’s easy for business to see how cloud-based data storage and computing can significantly lower the costs involved for SMB BC/DR while greatly improving efficiency, mobility, and collaboration capabilities.

Contact Us

  • (+353)(0)1-443-3807 – IRL
  • (+44)(0)20-7193-9751 – UK

Check our similar posts

Disadvantages of Spreadsheets – Obstacles to Compliance in the Healthcare Industry

Most of the regulatory compliance issues we talked about concerning spreadsheets have been related to financial data. But there are other kinds of data that are stored in spreadsheets which may also cause regulatory problems in the future.

In the US, a legislation known as HIPAA or Health Insurance Portability and Accountability Act is changing the way health care establishments and practitioners handle patient records. The HIPAA Privacy Rule is aimed at protecting the privacy of individually identifiable health information a.k.a. protected health information (PHI).

Examples of PHI include common identifiers like a patient’s name, address, Social Security Number, and so on, which can be used to identify the patient. HIPAA covers a wide range of health care organisations and service providers, including: health plan payers, health care clearing houses, hospitals, doctors, dentists, etc.

To protect the confidentiality, integrity, and availability of PHI, covered entities are required to implement technical policies such as access controls, authentication, and audit controls. These can easily be implemented on server-based systems.

Sad to say, many health care organisations who have started storing data electronically still rely on spreadsheet-based systems. Those policies are hard to implement in spreadsheet-based systems, where files are handled by end-users who are overloaded with their main line of work (i.e. health care) and have very little concern for data security.

In some of these systems, spreadsheet files containing PHI may have multiple versions in different workstations. Chances are, none of these files have any access control or user authentication mechanism whatsoever. Thus, changes can easily be made without proper documentation as to who carried out the changes.

And because the files are normally easily accessible, unauthorised disclosures – whether done intentionally or accidentally – will always be a lingering threat. Remember that HIPAA covered entities who are caught disclosing PHI can be fined from $50,000 up to $500,000 plus jail time.

But that’s not all. Through the HITECH Act of 2009, business associates of covered entities will now have to comply with HIPAA standards as well. Business associates are those companies who are performing functions and services for covered entities.

Examples of business associates are accounting firms, law firms, consultants, and so on. They automatically need to comply with the standards the moment they too deal with PHI.


More Spreadsheet Blogs


Spreadsheet Risks in Banks


Top 10 Disadvantages of Spreadsheets


Disadvantages of Spreadsheets – obstacles to compliance in the Healthcare Industry


How Internal Auditors can win the War against Spreadsheet Fraud


Spreadsheet Reporting – No Room in your company in an age of Business Intelligence


Still looking for a Way to Consolidate Excel Spreadsheets?


Disadvantages of Spreadsheets


Spreadsheet woes – ill equipped for an Agile Business Environment


Spreadsheet Fraud


Spreadsheet Woes – Limited features for easy adoption of a control framework


Spreadsheet woes – Burden in SOX Compliance and other Regulations


Spreadsheet Risk Issues


Server Application Solutions – Don’t let Spreadsheets hold your Business back


Why Spreadsheets can send the pillars of Solvency II crashing down

?

Advert-Book-UK

amazon.co.uk

?

Advert-Book-USA

amazon.com


2015 ESOS Guidelines Chapter 1 ? Who Qualifies

The base criteria are any UK undertaking that employs more than 250 people and/or has a turnover in excess of ?50 million and/or has a balance sheet total greater than ?43 million. There is little point in attempting to separate off high polluting areas. If one corporate group qualifies for ESOS, then all the others are obligated to take part too. The sterling equivalents of ?38,937,777 and ?33,486,489 were set on 31 December 2014 and apply to the first compliance period.

Representatives of Overseas Entities

UK registered branches of foreign entities are treated as if fully UK owned. They also have to sign up if any overseas corporate element meets the threshold no matter where in the world. The deciding factor is common ownership throughout the ESOS system. ecoVaro appreciates this. We have seen European companies dumping pollution in under-regulated countries for far too long.

Generic Undertakings that Could Comply

The common factor is energy consumption and the organisation’s type of work is irrelevant. The Environmental Agency has provided the following generic checklist of undertakings that could qualify:

Limited Companies Public Companies Trusts
Partnerships Private Equity Companies Limited Liability Partnerships
Unincorporated Associations Not-for-Profit Bodies Universities (Per Funding)

Organisations Close to Thresholds

Organisations that come close to, but do not quite meet the qualification threshold should cast their minds back to previous accounting periods, because ESOS considers current and previous years. The exact wording in the regulations states:

?Where, in any accounting period, an undertaking is a large undertaking (or a small or medium undertaking, as the case may be), it retains that status until it falls within the definition of a small or medium undertaking (or a large undertaking, as the case may be) for two consecutive accounting periods.?

Considering the ?50,000 penalty for not completing an assessment or making a false or misleading statement, it makes good sense for close misses to comply.

Joint Ventures and Participative Undertakings

If one element of a UK group qualifies for ESOS, then the others must follow suit with the highest one carrying responsibility. Franchisees are independent undertakings although they may collectively agree to participate. If trusts receive energy from a third party that must do an ESOS, then so must they. Private equity firms and private finance initiatives receive the same treatment as other enterprises. De-aggregations must be in writing following which separated ESOS accountability applies.

How DevOps oils the Value Chain

DevOps ? a clipped compound of development and operations – is a way of working whereby software developers are in a team with project beneficiaries. A client centred approach extends the project plan to include the life cycle of the product or service, for which the software is developed.

We can then no longer speak of a software project for say Joe?s Accounting App. The software has no intrinsic value of its own. It follows that the software engineers are building an accounting app product. This is a small, crucially important distinction, because they are no longer in a silo with different business interests.

To take the analogy further, the developers are no longer contractors possibly trying to stretch out the process. They are members of Joe?s accounting company, and they are just as keen to get to market fast as Joe is to start earning income. DevOps uses this synergy to achieve the overarching business goal.

A Brief Introduction to OpsDev

You can skip this section if you already read this article. If not then you need to know that DevOps is a culture, not a working method. The three ?members? are the software developers, the beneficiaries, and a quality control mechanism. The developers break their task into smaller chunks instead of releasing the code to quality control as a single batch. As a result, the review process happens contiguously along these simplified lines.

Code QC Test ? ? ?
? Code QC Test ? ?
? ? Code QC Test ?
? ? ? Code QC Test
Colour Key Developers Quality Control Beneficiary

This is a marked improvement over the previously cumbersome method below.

Write the Code ? Test the Code ? Use the Code
? Evaluate, Schedule for Next Review ?

Working quickly and releasing smaller amounts of code means the OpsDev team learns quickly from mistakes, and should come to product release ahead of any competitor using the older, more linear method. The shared method of working releases huge resources in terms of user experience and in-line QC practices. Instead of being in a silo working on its own, development finds it has a richer brief and more support from being ?on the same side of the organisation?.

The Key Role that Application Program Interfaces Play

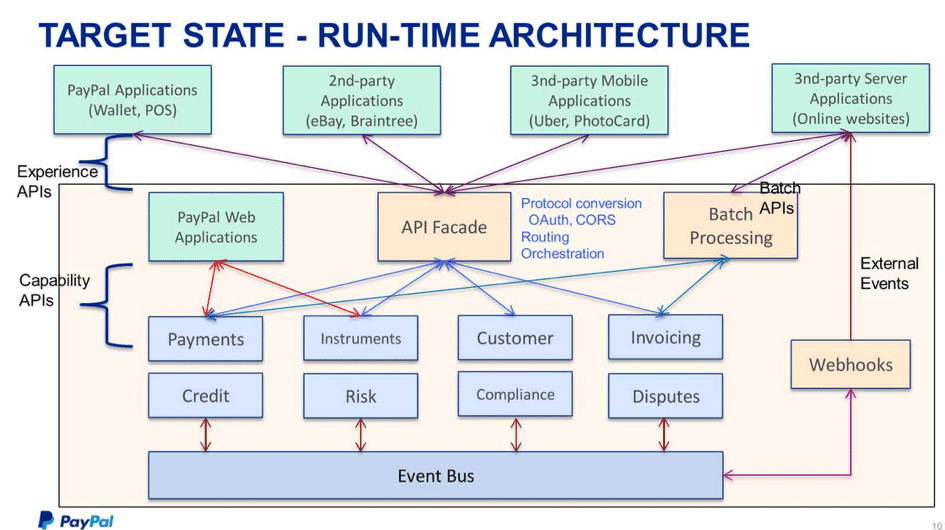
Application Program Interfaces, or API?s for short, are building blocks for software applications. Using proprietary software-bridges speeds this process up. A good example would be the PayPal applications that we find on so many websites today. API?s are not just for commercial sites, and they can reduce costs and improve efficiency considerably.

The following diagram courtesy of TIBCO illustrates how second-party applications integrate with PayPal architecture via an API fa?ade.

Working quickly and releasing smaller amounts of code means the OpsDev team learns quickly from mistakes, and should come to product release ahead of any competitor using the older, more linear method. The shared method of working releases huge resources in terms of user experience and in-line QC practices. Instead of being in a silo working on its own, development finds it has a richer brief and more support from being ?on the same side of the organisation?.

imgd2.jpg

The DevOps Revolution Continues ?

We close with some important insights from an interview with Jim Stoneham. He was general manager of the Yahoo Communities business unit, at the time Flickr became a part. ?Flickr was a codebase,? Jim recalls, ?that evolved to operate at high scale over 7 years – and continuing to scale while adding and refining features was no small challenge. During this transition, it was a huge advantage that there was such an integrated dev and ops team?

The ?maturity model? as engineers refer to DevOps status currently, enables developers to learn faster, and deploy upgrades ahead of their competitors. This means the client reaches and exceeds break-even sooner. DevOps lubricates the value chain so companies add value to a product faster. One reason it worked so well with Flickr, was the immense trust between Dev and Ops, and that is a lesson we should learn.

?We transformed from a team of employees to a team of owners. When you move at that speed, and are looking at the numbers and the results daily, your investment level radically changes. This just can’t happen in teams that release quarterly, and it’s difficult even with monthly cycles.? (Jim Stoneham)

Contact Us

  • (+353)(0)1-443-3807 – IRL
  • (+44)(0)20-7193-9751 – UK

Ready to work with Denizon?